

Table of Contents
Endpoint security decisions show up in ordinary work: employee laptops, remote access, file shares, cloud apps, helpdesk tickets, maintenance windows, and customer access. The EDR vs antivirus choice matters because studies estimate roughly 90% of successful cyberattacks and 70% of successful data breaches originate at endpoint devices.
This is not only a technical question. It affects how quickly your team sees risk, contains disruption, documents action, and keeps work moving. At Tech Advisory Group, we help you translate security tools into plain-English decisions about tickets, endpoints, monitoring, and escalation paths.
Jason Harlam, Business Development Manager at Tech Advisory Group, notes: “The right endpoint tool should make the next ticket easier to understand, not just add another alert for someone to sort through under pressure.”
EDR Vs Antivirus And The Security Decision Your Endpoints Force Every Day
Before you approve a renewal, security budget, or vendor change, ask how each tool affects daily operations. Your endpoint strategy should reduce repeat issues, give support teams useful detail, and help managers act when a laptop, file share, or cloud login behaves abnormally.
-
Traditional antivirus scanning: Looks for known malware patterns and blocks common threats on workstations and servers.
-
EDR adds context: Tracks behavior across endpoints, so support can see what happened before and after an alert.
-
Visibility shapes response: Better detail helps triage a ticket, escalate cleanly, and decide whether to isolate a device.
-
Business impact matters: Choose based on downtime, approval paths, monitoring needs, and unresolved risk.
EDR Vs Av In Daily Support And Incident Response Workflows
A remote employee opens a suspicious attachment before a customer proposal deadline, then the laptop starts launching unknown processes. The helpdesk needs more than a yes-or-no malware result. With EDR vs AV, the practical difference appears in triage, escalation, containment, and follow-up notes showing who did what and when.
That process matters because ransomware actors successfully disabled security solutions in 48% of their attacks last year. During business hours, our team reviews the alert, checks device activity, escalates complex cases to the right specialist, and keeps communication clear through resolution. Emergency support is available on nights, weekends, and holidays when needed.
A useful workflow includes a blocked executable, an isolated laptop, a ticket note showing what was touched, manager approval for containment, and a same-day status update so the business knows what happens next.
AV vs EDR Through The Lens Of Business Cost And Risk
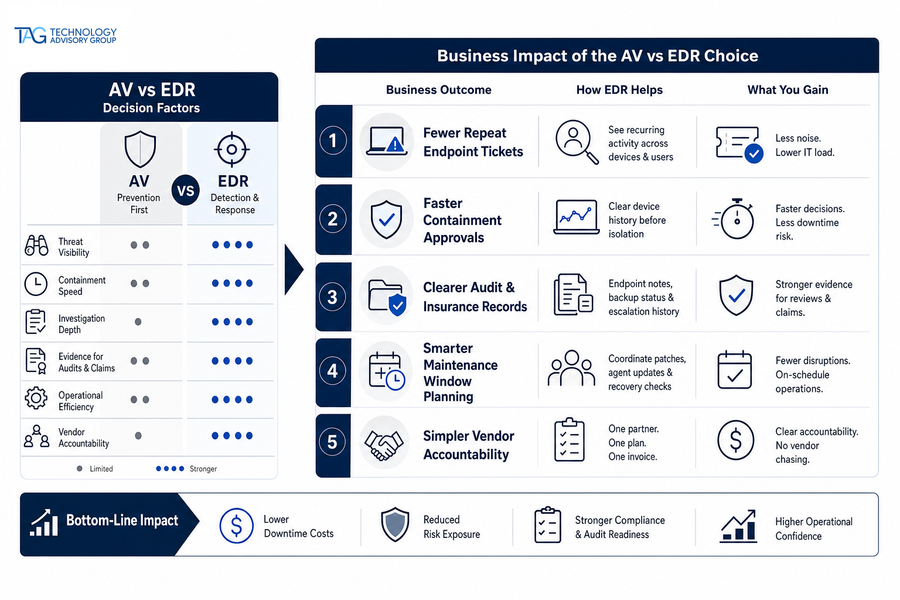
Endpoint security choices affect more than malware blocking. The av vs edr decision influences downtime, approvals, compliance evidence, invoice clarity, and whether leadership trusts the response plan.
-
Fewer repeat endpoint tickets: Better visibility helps identify recurring suspicious activity on the same laptop or user profile, instead of only closing the alert and waiting for the next helpdesk request.
-
Faster containment approvals: When malware prevention drops to 60%, response teams need clear device history before approving isolation, account disablement, or user access changes.
-
Clearer audit and insurance records: Endpoint notes, backup status, and escalation history give you evidence for reviews, claims, and compliance questions without rebuilding the timeline from scattered emails.
-
Smarter maintenance window planning: Our projects, cybersecurity, and backup teams coordinate patches, agent updates, and recovery checks around production schedules.
-
Simpler vendor accountability: With MSP, cybersecurity, procurement scoping, and backup management under one invoice, you avoid chasing separate vendors when ransomware prevention varies, including BlackByte at 26% prevention, BabLock at 34% prevention, and Maori at 41% prevention.
Related Endpoint Security Reads
Antivirus Vs EDR For Monitoring Maintenance And Executive Visibility
Security becomes easier to manage when you can see what is happening across endpoints without reading every technical alert. The antivirus vs EDR discussion should include monitoring, alert review, patch coordination, backup checks, and planning cadence.
That visibility matters when over 21% of connected enterprise devices have known vulnerabilities, and nearly 40% of devices registered in Active Directory lack proper EDR/XDR coverage. We use proactive monitoring, regular in-person system reviews, assigned vCIO oversight, and daily, monthly, and quarterly IT and satisfaction reviews to turn alerts into decisions about tickets, maintenance windows, backup health, and risk priorities.
The next step is to define what you need to see, who needs to act, and how often leadership needs reporting.
Endpoint coverage, patch status, backup health, and open security issues should all roll into the same operating view.
Strengthen Endpoint Decisions
Unsure whether antivirus or EDR fits your operations? Tech Advisory Group can help align endpoint security with support, monitoring, and response needs.
Antivirus Vs Endpoint Protection Steps Before You Renew Another Tool
Changing security tools affects users, support teams, approvals, and budgets, so review your operating reality before signing another renewal. The antivirus vs endpoint protection decision should start with endpoints, tickets, ownership, recovery, and reporting, not only software features. Our assessments, engineering and procurement scoping, flexible a la carte pricing, and customization help you match the toolset to your environment, with a 30-day opt-out clause after the first six months.
-
Inventory every endpoint: Include company laptops, shared workstations, servers, and personal devices used for work, since 85% of employees say company-issued devices are secured, while only 49% say the same for personal devices.
-
Review tickets and alerts: Look for repeat infections, failed updates, blocked apps, false positives, and unresolved alerts.
-
Map response ownership: Decide who approves isolation, escalation, user communication, customer access changes, and after-hours emergency involvement.
-
Confirm recovery and reporting needs: Validate backup status, restore paths, procurement options, and the monthly or quarterly security updates leadership wants to see, especially because misconfigured or missing EDR solutions affected over 25% of all incidents for the quarter.
Build Endpoint Security Around The Way Your Business Actually Operates
Endpoint security should reduce recurring issues, speed up response, clarify ownership, and improve planning for laptops, servers, remote users, file shares, backups, and approvals.
At Tech Advisory Group, we bring over 25 years of experience, a 100 percent local team, proactive monitoring, clear communication, and in-person reviews to help you evaluate what your current tools are doing across more than 1,512 managed endpoints.
If you want a practical review before your next renewal or security project, contact us and we will help you make the next decision with better operational visibility.
Explore Expert Cybersecurity Services Near You
Schedule Your Cloud Services Consultation
Ready to make a move to the cloud? TAG is ready to help with any or all cloud services from a private cloud, public cloud, or Microsoft 365 services.