

Table of Contents
Security vendors often use EDR, MDR, and XDR as if they mean the same thing. They do not, and that difference matters before you approve a budget, sign a contract, or ask your internal team to absorb another dashboard.
Jason Harlam, Business Development Manager at Tech Advisory Group, notes: “Start by asking who owns the alert after it fires, because security value depends on investigation, containment, documentation, and clear next steps.”
The practical MDR vs EDR decision changes who handles endpoint alerts, how tickets get prioritized, when escalation happens, and how long a device remains risky. Misconfigured or missing EDR solutions affected over 25 percent of all incidents for the quarter, which is why tool selection and operational follow-through belong in the same conversation.
Tech Advisory Group’s point of view is straightforward: start by asking who owns the alert after it fires, because security value depends on investigation, containment, documentation, and clear next steps.
MDR Vs EDR At A Practical Level
The first decision is not which acronym sounds stronger. It is whether you have the people and process to act when endpoint software flags a laptop, server, or shared workstation.
-
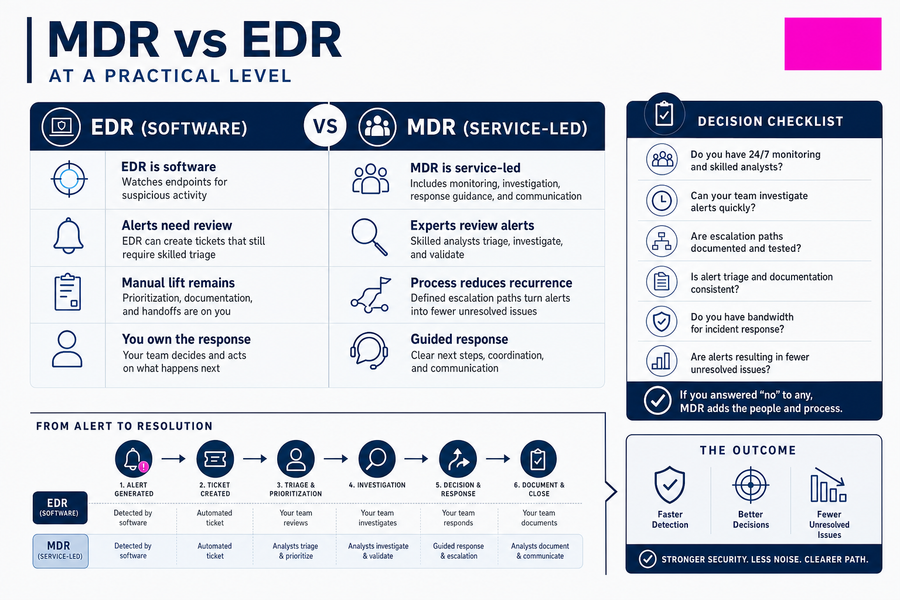
EDR is software: It watches endpoints for suspicious activity, such as unusual file changes, unexpected PowerShell activity, or abnormal access to shared files.
-
MDR is service-led: It adds monitoring, investigation, response guidance, and communication around next steps.
-
Alerts need review: EDR can create tickets that still require skilled triage and documentation.
-
Process reduces recurrence: MDR adds defined escalation paths so alerts become fewer unresolved issues over time.
EDR Vs MDR In Daily Operations
EDR stands for Endpoint Detection and Response. It is software installed across laptops, desktops, and servers to watch behavior, flag suspicious activity, isolate a device, or trigger automated actions. In an EDR vs MDR discussion, EDR produces alerts someone must review.
Endpoint visibility protects service reliability because one infected laptop can interrupt invoice processing, customer service notes, payroll files, or shared drives. Cybercriminals launched a monthly average of 2.8 million malware, adware, or unwanted software attacks targeting mobile devices. With over 1,512 endpoints managed, we see the practical side every day: alerts become tickets, tickets need priority, and unresolved tickets create business risk.
-
Behavior monitoring: Spots unusual actions on endpoints.
-
Automated containment: Can isolate a device when activity crosses a defined threshold.
-
Ticket creation: Sends alerts into a queue that needs ownership and follow-through.
EDR MDR Side By Side
The difference becomes clearer when you view ownership, response, and business impact together. A practical EDR MDR comparison should show what happens after an alert enters the ticket queue, who makes the decision, and how quickly normal work resumes.
|
Decision Area |
EDR |
MDR |
Business Impact |
|---|---|---|---|
|
What it is |
Endpoint software |
Managed detection and response service |
Tool cost versus service scope |
|
Who watches alerts |
Internal staff |
Security analysts and process owners |
Fewer missed tickets and clearer responsibility |
|
Flagged activity |
Alert or automated action |
Investigation and guidance |
Faster containment decisions |
|
Internal workload |
Higher triage burden |
Shared response workload |
Better staff productivity |
|
Escalation process |
Must be defined internally |
Built into workflow |
Clearer approvals and handoffs |
|
Best fit |
Skilled internal team with time to review alerts |
Need for guided response and defined escalation |
Lower downtime risk and less confusion during incidents |
More Security Strategy Guides
MDR EDR Decisions By Business Risk
The wrong choice creates ownership gaps, not just software gaps. A practical MDR EDR decision should show where security affects cost control, continuity planning, and recurring IT issues. This is where vCIO guidance belongs: connecting endpoint findings to budgets, workflows, compliance needs, and recovery plans.
-
Alert fatigue and ticket backlog: Too many low-priority tickets delay review of real risk and reduce confidence that critical alerts are being handled.
-
Delayed containment after suspicious activity: A payroll laptop needs action before file access spreads. Unclear approvals keep risk active.
-
Unclear accountability during escalation: Define who approves isolation, vendor calls, user communication, and executive updates before an incident starts.
-
Higher internal staff workload: IT loses time on triage instead of projects, onboarding, patching, and service requests.
-
Compliance and continuity exposure: Only 40% of organizations expressed confidence that their backup and recovery solution can sufficiently protect critical digital assets in a disaster. Endpoint response needs to align with recovery evidence and continuity expectations.
MDR And EDR As A People Process
MDR usually builds on endpoint protection technology, then adds people who monitor, investigate, and guide response. That human layer matters when a weak password, unusual login, or unexpected script turns into a containment decision. Only 12% of dictionary passwords are strong enough to take more than a year to guess.
With over 25 years of experience and more than 75 active clients, we know response needs clear ownership, rapid escalation for complex cases, and communication until resolution. Technology matters, but business impact depends on who reviews the alert, opens the ticket, approves the action, and confirms the endpoint is safe.
What this looks like in practice: A finance employee’s laptop triggers a suspicious login alert. The endpoint is isolated, an internal ticket is opened, and the escalation path identifies who reviews payroll system access. Clear communication continues until the issue is documented and resolved.
How To Decide What Your Business Actually Needs
Changing security tools or adding managed services affects budget, workflows, and staff responsibilities. Start with current capability, not vendor terminology. A Security Assessment, paired with no-charge engineering and procurement scoping, gives you a practical view before you buy.
-
Inventory endpoints and systems: Include laptops, servers, cloud apps, and personal devices, since over 17% of employees use personal mobile devices for work without informing IT.
-
Review alert ownership: Identify who receives alerts, who investigates them, and where tickets sit when the first reviewer is unavailable.
-
Map approvals and escalation: Define isolation, notification, vendor involvement, and leadership updates before pressure starts.
-
Assess staff capacity: 85% of employees state employers secure company-issued devices, while only 49% say the same for personal devices used for work.
Choose the Right Security Fit
Not sure whether MDR or EDR matches your risk, team, and response needs? Tech Advisory Group can help you make the right call.
Where vCIO Guidance Fits
Endpoint security decisions should not sit only with technical staff or vendor sales teams. Leadership needs a plain-English view of exposure, including which alerts threaten billing, customer service, compliance evidence, or recovery timelines.
We assign a vCIO to oversee each client, with regular touchpoints that can include daily, monthly, and quarterly IT and satisfaction reviews. That rhythm connects technical findings to cost control, fewer surprises, and clearer executive decisions.
-
Translate alerts into risk: Show which tickets affect operations, customer commitments, regulated records, or critical systems.
-
Prioritize security investments: Balance tools, training, backup management, and response processes against practical risk.
-
Build a roadmap: Sequence improvements across multiple quarters so endpoint security, recovery planning, and workflows improve together.
Reality Check Before You Buy
Security buying gets harder when every product promises visibility, faster response, and simpler management. Data from the 2025 North America Threat Landscape Report shows a threat environment defined by pressure, with the United States accounting for roughly 93 percent of all recorded incidents in the Americas.
Tech Advisory Group brings over 25 years of experience, more than 75 active clients, and over 1,512 managed endpoints to security conversations that need technical depth and business context. Our a-la-carte pricing options and 30-day opt-out clause reduce lock-in concerns while you evaluate fit, costs, escalation paths, and service quality.
From there, evaluate the capabilities that affect your daily operations: Security Assessments, Endpoint Protection, Managed IT, vCIO guidance.
Pair The Right Security Tools With The Right Team
The right decision is not based on the acronym. It is based on matching endpoint technology with people, process, escalation, and clear communication when an alert affects a device, ticket, approval, or customer workflow.
Tech Advisory Group supports businesses in Rhode Island and surrounding cities with Cybersecurity, Managed IT, Security Assessments, and vCIO guidance, backed by over 25 years in business and an assigned vCIO model. Complex problems. Simple solutions. If you want that thinking applied to your security stack, contact us for a practical conversation or security assessment.
Explore Expert Cybersecurity Services Near You
Schedule Your Cloud Services Consultation
Ready to make a move to the cloud? TAG is ready to help with any or all cloud services from a private cloud, public cloud, or Microsoft 365 services.